About this post: Thanks to MalwareHunterTeam for flagging this sample. This analysis and write-up were produced by Claude (Opus 5.5), working as an agent in Claude Code on a REMnux analysis VM. Tools used: Malcat, capa, 7-Zip, The Sleuth Kit, pdf-parser, speakeasy, a sandboxed Wine setup with a fake server, Censys and ANY.RUN.
TL;DR
This ZIP is a spear-phishing kit built on 10 November 2026. Inside is a virtual disk containing what looks like a speech draft by economist Piroska Nagy Mohacsi for a euro-policy event in Frankfurt. Opening the “PDF” shows a real, well-written document, and at the same time a small program quietly asks a server what to run next. The decoy itself was generated by ChatGPT: it carries a signed “Content Credentials” label from OpenAI. The kit has a bug of its own, though. One file was given the wrong name, so this copy crashes before it ever contacts its server.
- Delivery: ZIP →
.vhdxvirtual disk → a shortcut dressed up as a PDF. - Decoy: a four-page speech draft on euro adoption. Embedded C2PA data says ChatGPT made it.
- Payload: a tiny downloader that fetches
hxxps[://]2jcoasr[.]top/starcraftand runs whatever text comes back as a hidden command. - Hiding tricks: a hidden folder, a window-less console, a server address scrambled with a key that only arrives on the command line, and a “can I reach reddit?” check first.
- Broken as shipped: the program asks for
asdeqasd.dll, but the file on the disk is namedhorialhsdk.dll.
Piroska Nagy Mohacsi is named only because the lure uses her name. Nothing suggests she or her organisations are involved.
A disk inside a ZIP
The ZIP holds one 100 MB file, Piroska_Nagy_Mohacsi_Opening_Remarks.vhdx. A VHDX is a virtual hard disk: on Windows, double-clicking it mounts it as a new drive, much like plugging in a USB stick. Attackers like this format because it gets past email filters that only look at the outer archive. Depending on how up to date Windows is, files inside a mounted disk may also miss the “downloaded from the internet” warning label.
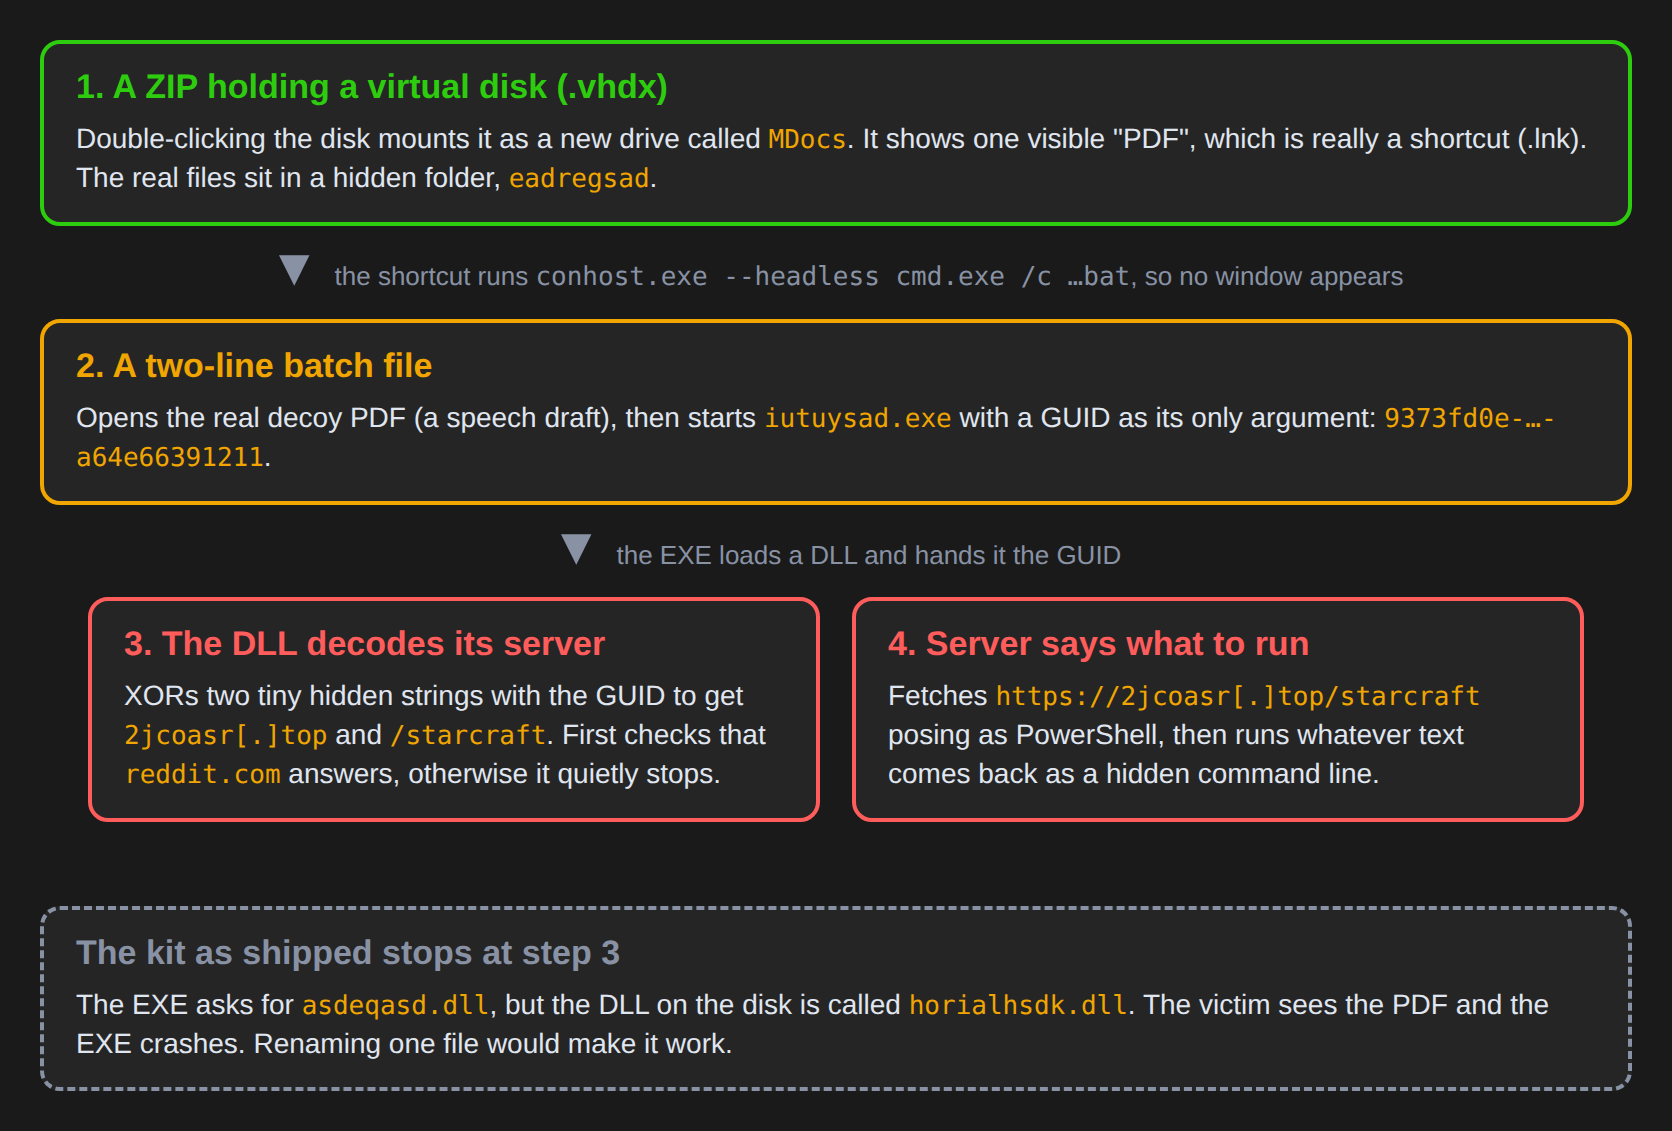
The mounted drive is called MDocs. It shows a single item, Piroska_Nagy_Mohacsi_Opening_Remarks, with a generic document icon. It is not a PDF but a Windows shortcut (.lnk). Next to it sits a folder called eadregsad, marked hidden and system, so a normal Explorer window won’t show it.
One click, two things happen
The shortcut runs this command:
conhost.exe --headless cmd.exe /c .\eadregsad\Piroska_Nagy_Mohacsi_Opening_Remarks
conhost --headless starts the command prompt without a visible window. That command prompt runs a two-line batch file from the hidden folder:
startthe real PDF, so the victim sees exactly what they expected.- Run
iutuysad.exe 9373fd0e-5eb0-49af-9e08-a64e66391211.
The long GUID in the second line matters, as the next sections show.
The decoy: written by ChatGPT, and signed to prove it
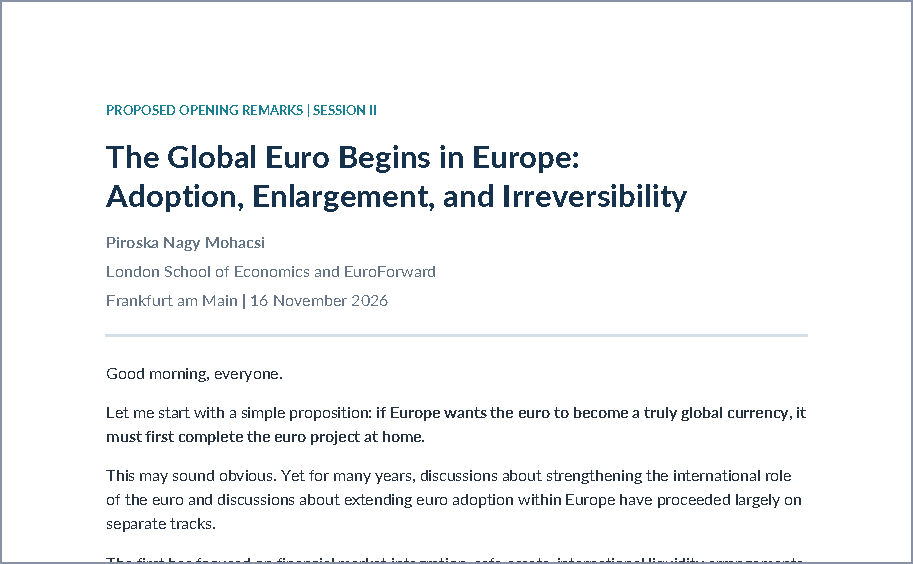
The decoy is a convincing four-page “Proposed Opening Remarks” speech, The Global Euro Begins in Europe: Adoption, Enlargement, and Irreversibility. It is credited to Piroska Nagy Mohacsi (London School of Economics and EuroForward) and dated Frankfurt am Main, 16 November 2026, six days after the kit was built. Slovakia, Bulgaria and Sweden come up as case studies. Whoever receives this probably works in or around European monetary policy.
The PDF also carries an embedded file called “Content Credentials”. This is a C2PA manifest, an industry-standard label that AI tools and cameras attach to say where content came from. This one says:
- created by: ChatGPT, model
gpt-6-thinking - type:
trainedAlgorithmicMedia, i.e. AI-generated - when: 2026-11-10 19:30:45 UTC
- signed by: an “OpenAI Media Service” certificate
The label is not just text. Its hash matches the PDF’s bytes, and the signature checks out against OpenAI’s certificate chain, so ChatGPT really did produce this file. We can’t prove who was typing the prompts. The timeline makes the operator the obvious candidate, though: the payloads were compiled about half an hour later. Many attackers have started using AI-written lures. It is unusual for a lure to carry signed proof of that.
The downloader: two small files, one key
iutuysad.exe is about 100 KB and does very little. It loads a DLL, looks up a function called horialhsdk in it, and passes that function the GUID from the command line.
The DLL horialhsdk.dll is where the work happens:
- Reachability check. It visits
hxxps[://]reddit[.]com/. If that fails (no internet, or a sandbox with networking cut off), it silently stops. This is a cheap way to avoid running inside offline analysis systems. - Unscramble the server. Two short strings are stored XOR-scrambled, using the GUID as the key. XOR scrambling simply flips bits according to a key; applying the same key again restores the original. Here, that gives
2jcoasr[.]topand/starcraft. Our own string-extraction tools found no trace of it; we had to read the decoding code and apply the GUID ourselves. - Ask the server. It sends a GET over HTTPS on port 443 and ignores certificate errors. Its User-Agent pretends to be PowerShell:
Mozilla/5.0 (Windows NT; Windows NT 10.0; de-DE) WindowsPowerShell/5.1.19041.5737. - Run the answer. It removes line breaks from the reply and runs it as a command line, with no window. It doesn’t even check whether the server answered with an error page.
There is no persistence and nothing else hidden in the DLL. The real next step lives on the server, which can hand out a different command at any time. That design keeps the files on disk small and bland.
One wrong file name: why this copy goes nowhere
iutuysad.exe asks Windows for asdeqasd.dll. The DLL on the disk is called horialhsdk.dll. Windows finds no such file. The program never checks that the load worked, so it jumps to address zero and crashes, and the victim may see a Windows error dialog next to the decoy.
This isn’t a renamed file. The DLL’s own internal name is horialhsdk.dll, and the disk’s change journal records no renames. The builder simply put the wrong name in the EXE. That makes it likely that other builds from the same kit work fine.
To check the rest of the chain, we ran it in an isolated Wine setup with no real internet:
- As shipped: the EXE crashes, executing address zero.
- With the DLL given the expected name: we answered with a local fake server, and the DLL decoded the address and sent
GET /starcraftwith the fake PowerShell User-Agent. It then ran our harmless test command (echo ORACLE_OK) as a hidden process.
For that test we also forced the reddit check to pass and moved the port. A normal request to reddit.com with the sample’s User-Agent gets a 200 response, so on a real victim machine that gate would usually pass.
A server set up the same afternoon
Everything about 2jcoasr[.]top points to a one-day build:
| When (UTC, 10 Nov 2026) | What |
|---|---|
| 11:54 | Domain registered |
| 19:30 | ChatGPT creates the decoy PDF |
| 19:47 | HTTPS certificate issued (Let’s Encrypt) |
| 20:01 | EXE and DLL compiled |
| 20:04 | Virtual disk and ZIP assembled, within about 30 seconds |
The domain resolves to 217[.]60[.]196[.]158 in Frankfurt. The address is routed by OVH and registered to a Dubai-based company, GOLD IP L.L.C-FZ.
A likely twin next door
The neighbouring address, 217[.]60[.]196[.]157, hosts cxittro[.]top, and the two look like a matched pair:
- registered 90 seconds after
2jcoasr[.]top(11:55:46 vs 11:54:16 UTC), with the same registrar name servers; - its Let’s Encrypt certificate was issued about ten minutes after ours (19:57 vs 19:47 UTC), also covering a single name;
- the same SSH and nginx versions;
- byte-identical error pages.
We think it was set up in the same batch, probably as a spare or for another target. No sample we’ve seen points to it yet, so treat it as a lead to watch rather than a confirmed indicator.
What we couldn’t see
- The second stage. Whatever
/starcrafthands out decides what this attack actually does. At the time of our investigation, the command has either been taken down or is only served to chosen targets.
Advice
For everyone:
- Be wary of a “document” that arrives as a disk image (
.vhdx,.vhd,.iso,.img). - If Explorer shows a “PDF” as a Shortcut, don’t open it.
- Turn on file extensions in Explorer.
For defenders:
- Alert on
conhost.exe --headlessstartingcmd.exe, especially from a newly mounted drive letter. - Hunt proxy logs for the
WindowsPowerShell/5.1.19041.5737+de-DEUser-Agent coming from processes that aren’t PowerShell. The downloader uses the system proxy, so the string will show up there. - Consider blocking automatic mounting of VHD/VHDX attachments for users who don’t need it.
- Watch for a short HTTPS request to reddit.com immediately followed by a request to a fresh
.topdomain.
Indicators
| Type | Indicator | Note |
|---|---|---|
| Domain | 2jcoasr[.]top |
Command server |
| URL | hxxps[://]2jcoasr[.]top/starcraft |
Returns the command to run |
| IP | 217[.]60[.]196[.]158 |
Command server host |
| User-Agent | Mozilla/5.0 (Windows NT; Windows NT 10.0; de-DE) WindowsPowerShell/5.1.19041.5737 |
Fake PowerShell UA |
| SHA256 | afd1ba88447d99dcb17e72d357116546666dfc2cfa108adb3f3932bf5bd1a452 |
ZIP |
| SHA256 | 612ef208778bd278f4c1ca433997c5d6ebe0b0b548eefba3a98ad813b07d708c |
VHDX |
| SHA256 | 4f31b82cf7ab82a0b9e3106bfe826840ea6060579308cf8044a44406c97b5f39 |
Shortcut (.lnk) |
| SHA256 | 95cb8529d4bda4da6239b7ef34d0e0d16831229b1ec8a54beb5ca1b8be1c1bcf |
Batch file |
| SHA256 | 4c0de6b9fe79c0d339a3bb6fdf148259976d9e43824bc0332278dbb897f44c95 |
Decoy PDF |
| SHA256 | 4c383c5fc615364eefa019a75d4d5295dbffa6b05ce4c768d8a2df55b30ec5f9 |
iutuysad.exe |
| SHA256 | b37fe9a5ff3a03bc68c90c3fdf70a6b4a6fc31cfed44c519f550bd4066adcda8 |
horialhsdk.dll |
| Key | 9373fd0e-5eb0-49af-9e08-a64e66391211 |
GUID passed on the command line |
| Artefact | Volume label MDocs, hidden folder eadregsad, LNK machine ID DESKTOP-MOMHMVTT |
Builder traits |
Wrapping up
This kit is small but carefully put together: a disk image, a window-less shortcut, a polished AI-written decoy, and a downloader whose server only appears when the right key is supplied. It was let down by a single wrong file name, so the next build will probably work. If you have seen 2jcoasr[.]top, the /starcraft path or that PowerShell User-Agent in your logs, we’d like to hear about it.
Stay safe, and look twice at any “PDF” that opens from a virtual disk.